Read More


Recognized for AI Excellence at 2026 Globee® Awards - Read More

Maitray Gadhavi
Every organization that wants to be competitive today needs modern cloud applications. These apps are needed to scale, reduce costs, and leverage latest technologies like AI.
But regulated industries move differently.
A healthcare provider can't deploy a feature update the way a SaaS company can. A fintech platform doesn't have the freedom to experiment with infrastructure. Insurance companies and legal tech enterprises operate under layers of compliance that most software teams never encounter.
The challenge here isn't technology. Cloud infrastructure works the same whether you're in healthcare or hospitality. The challenge is finding a cloud application development partner who actually understands cloud application compliance requirements.
That's because cloud application development for regulated industries combines secure cloud engineering, compliance, domain expertise, and modernization for enterprise needs.
At Radixweb, we have served 1200+ regulated enterprises across financial services, healthcare, insurance, and legal technology. Our hands-on expertise, domain-specific understanding, and experience with cloud compliance for regulated industries is what makes us a preferred choice. We don't treat compliance as a constraint or retrofit it later. Instead, we engineer native cloud applications where compliance is built-in, right from the start.
Regulated enterprises need cloud application development services from partners who understand both development and compliance. Radixweb brings 26+ years of enterprise cloud app development experience specifically in regulated industries like healthcare, fintech, insurance, and legal tech. We deliver secure cloud application development for enterprises with pre-validated compliance frameworks, audited security standards (SOC 2 Type II, ISO 27001), and zero-downtime modernization strategies that remove regulatory friction. The result: compliant cloud application development that accelerates business.
| Aspect | Details |
|---|---|
| What this guide covers? | Why regulated industries face unique cloud app development challenges, why enterprises choose Radixweb for audit-ready cloud application development, how Radixweb delivers cloud application solutions for regulated industries |
| Who should read this guide? | CISOs evaluating cloud app development partners, CTOs in regulated sectors, IT directors looking for cloud app development services with regulatory alignment, founders and leaders of FinTech, HealthTech, InsurTech, Legal Tech, and data-first companies |
Most people assume that enterprise cloud application development for any industry works the same way. Sure, the frameworks are the same. The deployment patterns are the same. The technical aspects like containerization, orchestration, databases, and message queues don't change. And microservices work the same for ride-sharing apps and banking platforms.
But that's only part of the story. Where regulated industries diverge sharply is in security, compliance, and audit requirements. A SaaS company asks, "Will this scale?" A fintech company asks, "Will this pass a compliance audit?" A healthcare platform asks, "Does this protect patient data to HIPAA standards?"
Here's how enterprise cloud compliance requirements vary across regular and regulated industries:
| Aspect | Regular Industry Cloud Apps | Regulated Industry Cloud Apps |
|---|---|---|
| Security approach | Best practices, then audit | Compliance frameworks first, then architecture |
| Data handling | Optimize for performance | Balance performance with audit trails and access controls |
| Deployment strategy | Frequent, rapid releases | Planned releases with change management documentation |
| Infrastructure provisioning | Automated, minimal oversight | Infrastructure as code with full audit trails and approval workflows |
| Access controls | Role-based permissions | Role-based plus multi-factor authentication, biometrics, session controls, and continuous monitoring |
| Encryption | Data at rest and in transit | Data at rest, in transit, and in use, with key management audit trails |
| Incident response | Log and learn | Immediate notification, containment, forensics, mandatory regulatory reporting |
| Audit requirements | Annual reviews | Continuous audits, real-time compliance reporting, third-party assessments |
These differences ripple through every decision. They change how you architect data flows across the cloud. They affect your infrastructure choices. And they determine what gets logged, who can access what, and how encryption keys are handled.
This makes it clear why cloud application development for regulated industries requires understanding not just tech, but the industry-specific regulatory landscape too.
Over 26 years, Radixweb has built a deep practice in cloud-native application development for regulated industries. We're not a generalist shop that handles compliance as an add-on. We have:
Here are a few examples of our secure cloud application development for enterprises:
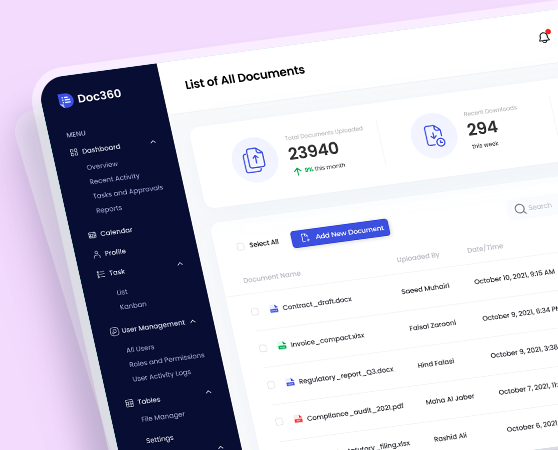
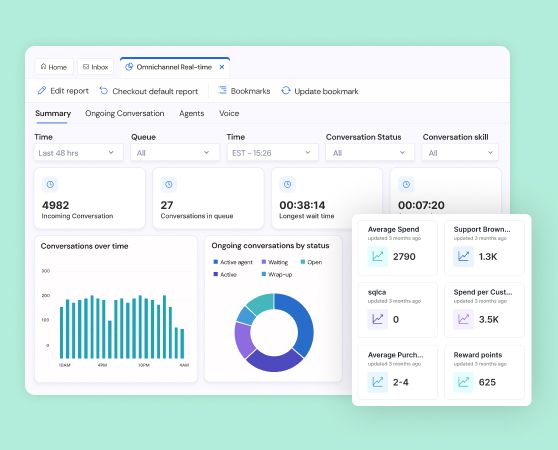
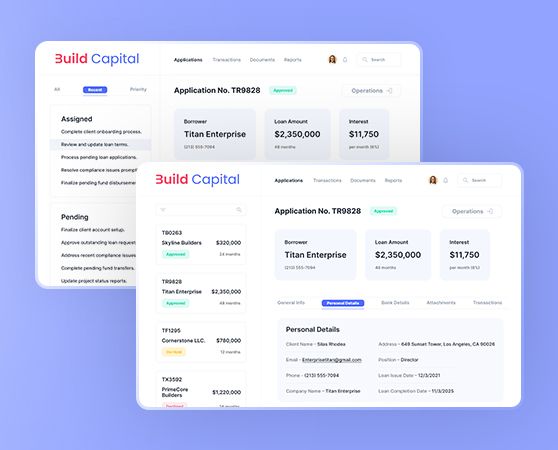
All these clients came to us with a similar underlying challenge. They all wanted to build cloud apps that were fast, secure, and audit-ready on day one. But their situations and constraints were different. And we've been able to successfully deliver success across all these engagements.
For regulated enterprises, Radixweb brings together cloud engineering expertise, domain-aware delivery, and the governance needed to build cloud-native applications that can scale, without compromising control. Here’s why we are a trusted choice for enterprise cloud app development.
When an enterprise in a regulated industry selects a cloud application development company, the vendor review process often takes longer than the actual project. InfoSec teams need proof. Compliance teams need documentation. Procurement needs audit trails.
Radixweb holds SOC 2 Type II compliance, which means we've been independently audited on our security controls, access management, and data protection practices over an extended period, not just a snapshot in time. We also maintain ISO 27001 certification (information security management) and ISO 9001 certification (quality management). These aren't marketing credentials. They're third-party proof that our security practices are audited, documented, and continuously maintained.
This matters because when your InfoSec team reviews Radixweb as a vendor, they don't start from zero. We've already passed the hardest tests. The procurement cycle that typically takes 3–6 months collapses to weeks because the heavy lifting is done.
Secure cloud app development for enterprises typically starts the same way: with discovery. Your team explains what you need to build. Our architects understand the requirements. Then they design the application architecture. This process typically takes 4–8 weeks.
But if you're the fifth healthcare company building a telemedicine platform, or the third fintech startup building a lending platform, or even the second insurance company modernizing claims processing, you know we've already built solutions that solve your challenges before. So, we can apply the same understanding of cloud application security for regulated industries to your project now.
We have pre-validated reference architectures and compliance templates for HIPAA-aligned healthcare data models. We have multi-tenant SaaS blueprints that satisfy PCI DSS requirements for fintech. We have event-driven architectures for insurance platforms that align with SOX and audit requirements.
These aren't one-size-fits-all templates though. They're just the starting points. We adapt them to your specific business logic, integrations, and data models. But instead of designing from first principles, we start with a framework that already embeds compliance, security controls, audit logging, and best practices. The outcome? Discovery time for cloud app development services drops from 6 weeks to 3.
There's a difference between a development team that has built cloud applications and a team that has spent decades solving problems in specific industries.
Radixweb has delivered 4,500+ projects for 3,000+ organizations across 30+ industries. This depth of experience across healthcare, fintech, insurance, and legal technology means we don't learn your industry on your dime. We know the regulatory landscape. We know the integration patterns. We know what breaks and how to prevent it.
A healthcare client doesn't need to explain HIPAA's Privacy Rule or the difference between de-identification and anonymization. We know that. An insurance company doesn't need to explain why claims processing needs multi-stage approval workflows and audit trails at every step. We've built it dozens of times.
This doesn't mean we know your industry better than you. It's just means we bring efficiency to the table. You get the right cloud-specific guidance based on your project's context, not a partner who joins a sprint with a blank slate.
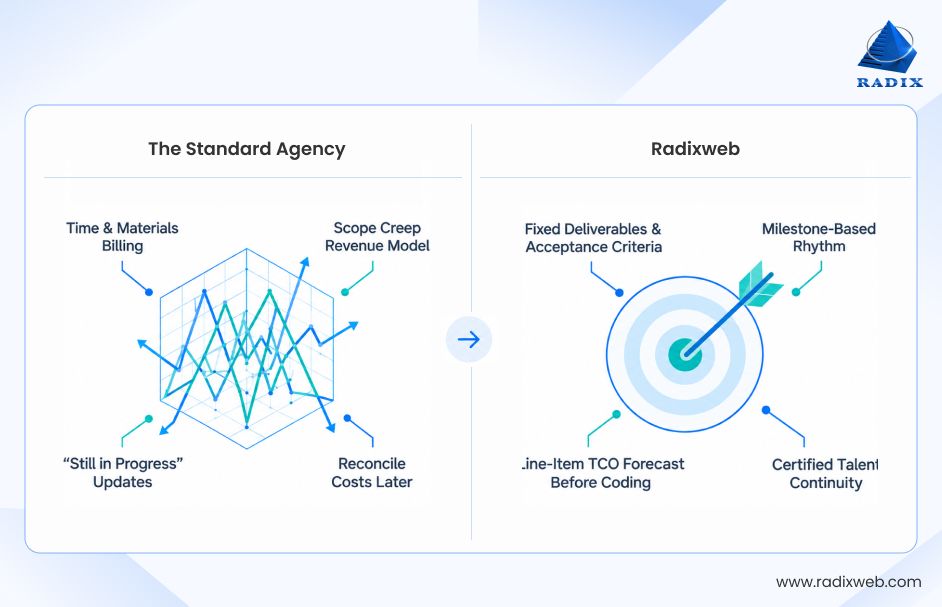
Cloud application development projects can evolve as requirements, compliance needs, and integrations become clearer. While time-and-materials engagements offer flexibility when scope is still taking shape, a fixed-cost model is often better suited to well-defined enterprise cloud projects where procurement teams need greater cost predictability.
At Radixweb, we structure fixed-cost engagements around clearly defined deliverables, milestone-based acceptance criteria, and a detailed Total Cost of Ownership (TCO) model covering compute, data transfer, managed services, licensing, and personnel. This gives stakeholders a transparent financial baseline before development begins.
But fixed cost isn't the only option. Our cloud application development services support multiple engagement models, including time-and-materials and other flexible approaches, so enterprises can choose the commercial structure that best fits their project's scope, uncertainty, and delivery needs.
Most enterprises in regulated industries didn't wake up with cloud applications. They inherited on-premises systems that worked fine for 10 years and now can't scale or adapt. Re-platforming these legacy systems is the right cloud migration strategy, but it's terrifying. You can't take down a healthcare platform for three months while you rebuild it. You can't interrupt a lending platform's operations while you migrate to the cloud.
This is where the strangler-fig pattern changes everything. Instead of rip-and-replace, we implement a phased approach. The legacy application stays online and revenue-generating while we build the new cloud-native architecture alongside it. Using feature flags and controlled cutovers, we gradually route traffic from the legacy system to the modern cloud application. Customers see no downtime. Operations continue uninterrupted.
We've done this dozens of times. And the point isn't just zero downtime during high traffic app migration. It's confidence. You know the old system keeps working if anything goes wrong. For regulated enterprises considering cloud modernization for regulated industries, this approach is often the only acceptable strategy.
Regulated Industry Cloud Applications & AI-ReadinessRegulated industries are moving to the cloud not only to modernize their applications, but also because cloud offers a scalable foundation for AI. With cloud infrastructure, it also becomes easier to access data across systems and introduce intelligent capabilities without rebuilding the application from scratch.As a result, modern, regulatory-compliant cloud applications increasingly need AI built into their architecture and workflows while existing cloud apps also need AI integrations.Radixweb is prepared for this shift with expertise across AI, ML, GenAI, agentic AI, and other emerging technologies, helping enterprises bring advanced intelligence into cloud applications while keeping security, governance, and enterprise requirements in focus.
These key reasons above explain why Radixweb maintains a 97% client retention rate and why our average enterprise engagement lasts five years or longer. For regulated enterprises, choosing a cloud app development partner means finding a team that can balance compliance, security, cost predictability, and evolving business requirements. That combination is what makes Radixweb a long-term technology partner for custom cloud application development in regulated industries.
Regulated industries come with distinct compliance requirements, operational workflows, and data security considerations. We bring this understanding into cloud app development, adapting architecture, integrations, and delivery approaches to the realities of each sector. Here are the key regulated industries where our experience is most relevant.
Compliance-focused cloud app development is a non-negotiable in healthcare. A HIPAA violation costs millions in fines and destroys reputation. This is why healthcare providers and HealthTech companies choose Radixweb for cloud application development for healthcare industry that doesn't compromise on compliance.
We bring pre-validated reference architectures for HIPAA-aligned cloud computing. We know the Privacy Rule (who can access what), the Security Rule (how to protect data), the Enforcement Rule (what happens when something goes wrong), and the Notification Rule (breach reporting). More importantly, we've embedded these requirements into application design.
What we deliver for healthcare:
Legacy healthcare systems running on 20-year-old infrastructure? We modernize them to cloud-native architectures without disrupting live patient care.
If healthcare is about patient safety, fintech is about financial safety. A transaction error, a data breach, a compliance miss can crater a company. We've completed over hundred fintech projects, making us one of the most experienced companies for cloud app development for fintech industry.
We offer secure cloud application development for enterprises looking for custom banking applications, billing and accounting software, auto finance platforms, debt collection software, and tax preparation software, all built around one principle: if it touches money, it gets audit-grade security and compliance.
Our fintech expertise covers:
We've modernized core banking platforms that handle billions in daily transactions. We've built lending platforms managing billions in active loans. We've engineered payment systems processing millions of transactions hourly. Every one of these systems was built for regulatory scrutiny.
Insurance companies operate under continuous regulatory scrutiny and audit. This is why we've built expertise in cloud application development for insurance industry that doesn't just survive audits, it was designed for them.
We deliver audit-ready financial platforms for insurers that withstand regulatory examination, continuous compliance checks, and scale requirements. Our work spans health insurance administration, claims processing, policy management, and risk assessment.
What we deliver for insurance:
Our insurance practice includes building systems for commercial insurers, health insurance companies, specialty insurers, and reinsurers. The common thread: complexity and compliance baked into the foundation.
Legal technology operates under some of the strictest confidentiality and audit requirements in any industry. A breach of attorney-client privilege isn't just a compliance violation, it's a fiduciary breach. This is why we offer secure, scalable, and 100% compliance-ready cloud application development for the legal industry.
We deliver modern cloud platforms for legal enterprises that require strict audit trails, access controls, and data confidentiality. Our legal tech platforms include case management systems, document automation, legal research platforms, billing and time tracking, and matter management tools.
Our legal tech expertise includes:
Some regulated industries don't fit the obvious buckets, but they share one critical need: data protection in cloud applications. This could be financial reporting platforms, biotech data repositories, energy trading systems, or telecommunications billing systems. They all have enterprise cloud compliance requirements and need to scale without sacrificing security.
For data-heavy regulated businesses, we deliver:
Across healthcare, fintech, insurance, legal tech, and data-heavy regulated industries, the pattern is consistent. We don't just build applications. We build data privacy compliance in cloud applications so that they pass audits, scale under pressure, and reduce regulatory friction over time.
Don't Let Compliance Slow You Down, Get Cloud Apps Developed with Radixweb
Regulated industries are moving to the cloud. To remain competitive, you need to do the same. But the question is whether you’ll do it with a partner who understands the regulatory landscape or someone who’ll build an app first and scramble to make it compliant later. That choice determines whether you are able to develop secure and scalable enterprise applications or compliance concerns keep slowing you down.At Radixweb, we’ve spent 26+ years building cloud-native applications for enterprises across regulated domains. We know what enterprise cloud application development demands in healthcare, fintech, insurance, and legal tech. That’s exactly why enterprises in regulated industries choose us as their cloud app development partner. The next step is simple: schedule a consultation with our cloud experts. We’ll review your current architecture, discuss your regulatory requirements, and outline a realistic secure cloud application development strategy. Without the hype, without the compromise.
Ready to brush up on something new? We've got more to read right this way.