Read More


Recognized for AI Excellence at 2026 Globee® Awards - Read More

Pratik Mistry
Global digital payments are projected to reach $37.45 trillion in 2026, embedded finance is expected to hit $197.06 billion, and about 350 million people now use neobanks. Investors are backing up products that hold up in production, not polished demos.
That shift raises the bar for fintech app development. Users judge a product on failed payments, settlement speed, and dispute resolution. Regulators expect audit trails that already exist. Investors expect unit economics that survive scale.
On a custom loan management platform we developed recently, the hardest problems sat beneath the screens. Document workflows, third-party data verification and decision traceability, plus handoffs between systems never designed to talk to each other.
Getting there takes more than engineering. The teams that ship well settle licensing, workflows, compliance and integrations early, then build. Below we will showcase how that plays out, step by step.
To develop a fintech app in 2027, start with the license model and money flows, not features. Choose the app type, design the ledger and workflows, build compliance and security into the architecture, connect banks and processors through abstracted APIs, and launch in phases. Expect $40,000 to $300,000 and three to twelve months, depending on scope, with AI applied to fraud, underwriting and operations.
| Column 1 | Column 2 |
|---|---|
| Aspect | Details |
| What does this guide cover? | Fintech app types, workflow and infrastructure design, compliance and security architecture, the build process, features, tech stack, API integrations, cost, partner selection and AI. |
| Who should read this guide? | Founders, CTOs, product heads and digital leaders at banks, lenders and insurers, plus companies adding embedded finance, and the compliance teams backing them. |
Fintech app development is the process of building secure digital applications for payments, banking, lending, investments, and financial management. It succeeds on four things: Trust, regulatory fit, transaction speed, and integration depth. Features come after these. A product weak on any one of the four rarely survives its pilot.
Users never read your security page. They notice whether a payment failed twice, whether a balance looked wrong for an hour, and how long support took to respond. Each of those moments traces back to decisions about retries, ledger design and observability.
The licenses you hold or borrow, the data you may store, and the regions you may serve shape the system before any code is written. Teams that discover this in month five rebuild onboarding, storage and reporting, and the delay often costs more than the original compliance work would have.
Real-time rails such as FedNow, SEPA Instant, and UPI have reset expectations. A two-day settlement window now reads as a defect, and it forces fraud and liquidity management into seconds.
One account-takeover wave can undo a year of brand work. Buyers in B2B finance now ask for SOC 2 reports and penetration test summaries before they ask for a demo, so security evidence is a sales asset as well as a control.
Most fintech products orchestrate banks, processors, KYC vendors, and data providers. Strong application integration for fintech platforms decides how fast you can enter a market, swap a failing provider, or add a product line.
Treat these four as a kickoff checklist. It is far cheaper than discovering them as production incidents.
Fintech apps fall into six groups. Payments, lending, digital banking, wealth and investment, insurance, and personal or business finance. Each carries a different regulatory burden, data model and risk profile, so one build plan cannot serve all of them.
| Type | What it demands most |
|---|---|
| Payments and wallets | Idempotent transactions, PCI DSS scope control, fraud scoring in the payment path |
| Lending and BNPL | Credit decision engines, bureau integrations, explainable underwriting, collections |
| Digital banking | Core banking or BaaS connectivity, ledger accuracy, card issuing, deposit rules |
| Wealth and investing | Market data feeds, order management, suitability checks, brokerage licensing |
| Insurtech | Policy administration, claims automation, actuarial rules, document-heavy workflows |
| Personal and business finance | Account aggregation, categorization accuracy, consent management |
The differences go deeper than the table suggests.
A payments app lives or dies on transaction integrity. Duplicate charges, lost callbacks, and unreconciled settlements are daily risks, so effort goes into idempotency, queues and reconciliation. Margins are thin, which makes processor fees, interchange and failed payment retries a financial concern as well as a technical one.
A lending product is a decisioning problem. Data ingestion from bureaus and bank accounts, a scoring engine that can explain its outputs to a regulator, loan servicing logic and a collections process that respects conduct rules. Underwriting data quality matters more than model sophistication, because bad inputs make explainability impossible.
A digital bank carries the heaviest operational load, with ledgers, card programmes, deposit rules and usually a sponsor bank or BaaS partner. Wealth platforms add market data and suitability rules, while Insurtech looks more like case management than payments. For Insurtech, the integration burden usually comes from brokers, carriers, and legacy policy systems, not from payment rails.
Remember That: The license model decides your build-versus-partner split. If you cannot hold the license, you will sit on a BaaS provider, and the architecture should stay provider-portable from day one.
Teams still shaping the concept can test early-stage fintech app strategies worth validating against current demand. Pick the type first. Team shape, budget and timeline follow from that choice.
Essential features of fintech applications include secure onboarding with KYC, multi-factor authentication, real-time transaction processing, notifications, clear history, fraud alerts, dispute handling and easy support access. Beyond that, features depend on product type.
Keep in Mind: Do not neglect the back office. The console used by operations, risk and support often decides whether the product runs profitably, yet first builds routinely under-scope it.
Start with this baseline and add differentiators once core flows settle. Retention features such as rewards, budgeting insights, and smart notifications work only when the transaction data underneath is accurate and timely.
Financial services companies are not the primary buyers of fintech app development in 2027. The embedded finance trend, financial services functionality built into non-financial products, means healthcare companies, real estate platforms, retailers, and agricultural businesses all need financial technology built into their core operations.
Patient payment portals, insurance premium collection, medical billing reconciliation and HIPAA-compliant financial data handling. A provider collecting patient payments holds PHI and PCI-scope data in one application, which demands dual compliance architecture. Every access to payment records needs an audit trail. Teams planning this should study considerations for building healthcare app before finalizing scope and data boundaries.
Rent collection platforms, security deposit escrow regulated by US state laws, title insurance and closing payment workflows, plus mortgage application and lender integrations. Fractional property investment, built on tokenized ownership, adds complex securities regulation to the standard fintech stack. Property businesses can speed delivery with custom real estate application solutions built around escrow, reporting and compliance needs.
Embedded BNPL at in-store and mobile checkout, loyalty points with monetary redemption value, merchant cash advances for working capital and supplier payment financing. Points redeemable for cash count as regulated financial instruments in some jurisdictions. Each feature carries its own compliance obligations. Retail teams should review retail app planning fundamentals before adding financial features to customer apps.
Embedded checkout financing, marketplace split payments, seller payouts, wallet balances and chargeback management. Platforms holding funds on behalf of sellers may trigger money transmission or licensing rules, depending on jurisdiction. Dispute handling and refund flows need clear ownership. Online businesses can build these capabilities through ecommerce app checkout and payments development that treats compliance and reconciliation as core features.
Crop insurance fintech, commodity financing, supply chain payment platforms for agricultural input suppliers, and cooperative payment systems for farmer collectives. Agricultural fintech is a growing category in emerging markets where traditional banking infrastructure is thin and mobile money adoption is high.
The compliance implication for non-financial companies building fintech features: the compliance requirements do not change because the primary business is not financial services.
A healthcare company building a patient payment portal still needs PCI DSS. A retailer embedding BNPL still needs consumer credit regulatory compliance. The sector context changes the user experience and the data model; the financial compliance requirements are determined by the financial activity, not the industry.
Before a fintech app moves into development, its financial workflows need to be designed on paper. Map the money movement first, then transaction states, exceptions and reconciliation points, and only then screen and code. If developers cannot see where every unit of currency sits at every moment, they build ambiguity into the product, and it resurfaces defects, support tickets and rework.
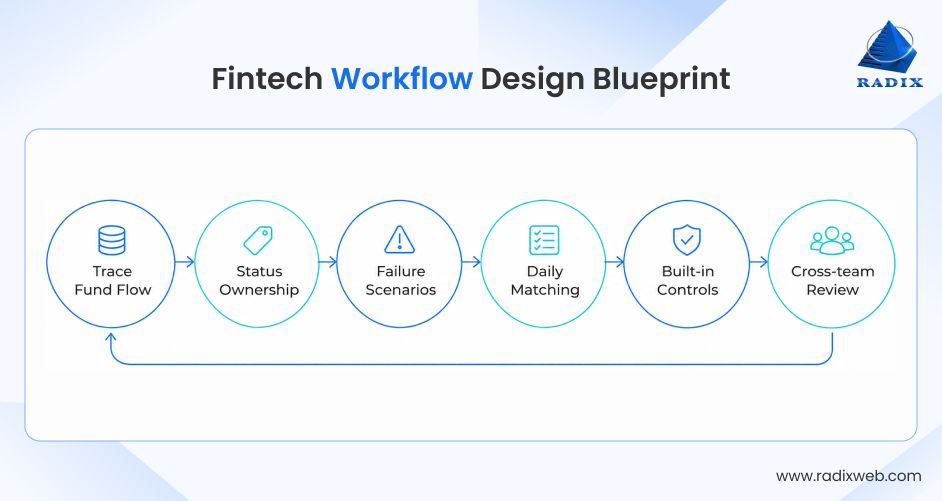
Identify who pays whom, through which rail, with which fees, and when each party treats funds as theirs. This exposes liquidity gaps and fee leakage early. Document every fee, hold period and currency conversion, because these details decide margin and support load later.
Initiated, authorized, pending, settled, failed, reversed, disputed. Each needs an owner, a timeout and a next action, otherwise transactions stall with nobody responsible. Time-based rules, such as automatic escalation after a set of delay, turn vague pending states into managed ones.
Partial payments, duplicate submissions, chargebacks, provider outages and mismatched amounts generate most support tickets, yet they are the least specified part of most requirements documents. Write each one as a scenario with an expected system response and a named human owner.
Decide how internal ledgers are matched against bank and processor statements, how breaks are detected, and who resolves them within what time. Define tolerance rules and ageing buckets for unmatched items, so finance teams see problems daily rather than at month's end.
Limits, approvals, dual authorization, and risk checks belong inside the workflow. Bolting them on later means re-testing every flow. Decide which controls operations can adjust through configuration and which stay fixed in code, so risk teams can change thresholds without a release.
Finance, risk and support staff see edge cases product teams miss. Put them in the room before development begins. Walk them through each state diagram, ask what breaks their day today, and record the answers as written requirements instead of verbal feedback.
Document each workflow as a state diagram with named owners and service-level targets for every pending state. For example, a payout stuck in pending for more than 24 hours should trigger an alert and a defined manual path, not a support ticket that bounces between teams.
Reviewing these diagrams with finance operations before development is the cheapest quality gate in the whole project. An hour spent on a settlement edge case here saves a sprint later.
Every fintech app rests on five layers. A ledger, payment rails and processors, identity and KYC services, a risk and fraud engine, and a data layer. Choosing these deliberately decides how fast you scale and how painful change becomes.
A double-entry, append-only ledger is the source of truth. Derive balances from immutable entries instead of overwriting a number. This makes audits, reversals, and reconciliation tractable. Corrections become new entries rather than edits, which gives auditors a complete history of every balance change.
Cards, ACH, wire, RTP, SEPA, and local schemes differ in timing, fees and failure modes. Abstract them behind an internal interface so a provider can be replaced without touching business logic. Keep fee logic, routing rules and retry policies in configuration, so finance teams can tune cost without deployment.
Document verification, sanctions of screening and ongoing monitoring should sit behind a vendor-agnostic service, since vendors change pricing and coverage. Store verification results and decision reasons centrally, so a vendor switch does not erase history, and compliance teams can reproduce any past onboarding decision.
Rules plus machine-learning scoring, evaluated before authorization rather than after money has moved. Keep rules editable by risk analysts without a release, log every decision with its inputs, and feed confirmed fraud outcomes back into the models, so detection improves over time.
Event streaming, a warehouse and clear lineage, so any figure shown to a regulator trace back to source events. Separate operational reporting from analytical workloads and apply the same access controls and retention rules to derived datasets as to the source records. Building this layer well takes scalable data engineering for financial pipelines, not a reporting add-on.
Topology matters as much as components. Multi-region deployment, queue-based processing and graceful degradation decide whether a provider outage stays minor. Understanding how client and server responsibilities divide also helps keep sensitive logic off the device.
Compliance architecture is the set of technical controls that make regulatory obligations enforceable by the system itself. Without it, an app can work perfectly and still fail to launch, because licensing partners and auditors will not sign off.
Sponsor banks, the licensed institutions behind many fintech products, review an app's controls before they approve its program. A missing control can delay launch by months. Understanding how application architecture is structured helps teams place each control where the system can enforce it.
Build a regulatory requirements matrix during discovery. Jurisdiction, product, license, obligation and the control that satisfies it. It becomes the launch checklist and audit map.
Fintech security goes beyond encryption and login. It covers transaction integrity, device and session trust, API protection, secrets management and monitoring, because attackers target money movement and account takeover, not just data.
Fraud rings test new products quickly, and a launch without velocity limits and device checks is often the first target.
Governance practices around safeguarding sensitive data and managing risk should be agreed at design stage, with threat modelling on every money-moving flow while changes are still cheap.
A scalable custom fintech app development process runs through discovery, compliance mapping, architecture, iterative build, testing, phased launch and continuous operation. Skipping discovery and compliance mapping is the most common reason timelines slip.
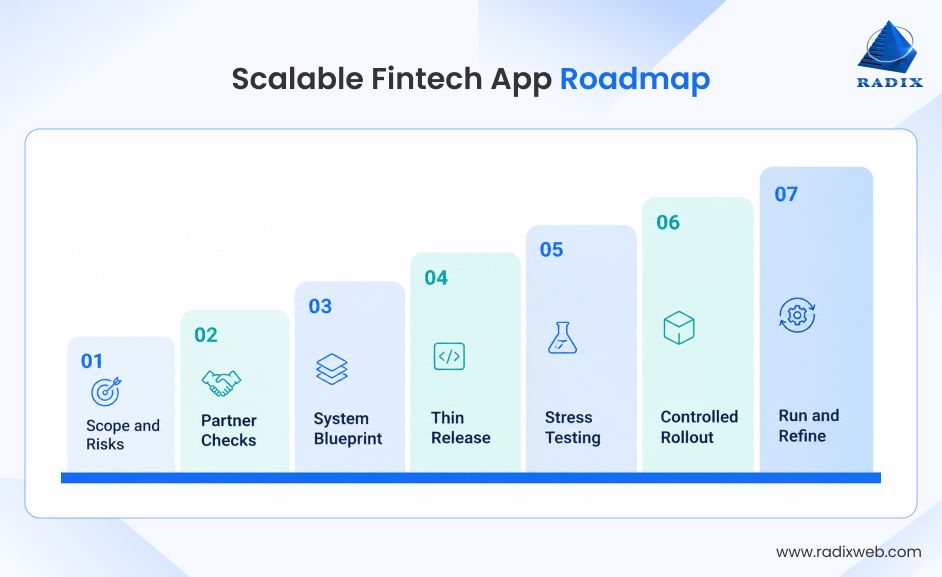
Define the target user, money flow, license position, and commercial model before any design work begins. Interview operations, risk, compliance and support stakeholders to surface constraints early. The output is a scoped roadmap, a risk register and an explicit list of what release one excludes, so the whole team shares one clear definition of done.
Confirm regulatory obligations first, then shortlist banking, KYC and processor partners. Check API maturity, sandbox quality, pricing and uptime history before committing. Ask each partner for production incident history, rate limits, webhook reliability and contractual exit terms, so a weak provider never becomes a single point of failure for your launch. Score every option consistently.
Most early products suit a modular monolith with clear domain boundaries, split later when scale demands. Define the ledger, data model and integration abstractions, and design UX around trust moments such as consent, confirmation and failure. Keep domain ownership clear. Review the architecture choices behind scalable mobile apps to keep services adaptable as volumes grow.
Ship the thinnest production slice that moves real money safely. Use provider sandboxes from the start and automate contract tests, so a provider-side change fails a test instead of a customer's payment. A fintech MVP delivery partner can quickly validate demand, compliance fit, core flows and unit economics before the full budget is formally committed.
Run load tests at several multiples of expected volume, chaos tests on provider failures and reconciliation and failover checks. Inject failures by dropping webhooks, delaying settlement files, and returning malformed responses, then confirm the ledger still balances. Add app penetration and security testing solutions to expose weaknesses in payment flows, APIs and sessions before attackers do.
Start with a closed cohort and conservative transaction limits. Watch authorization rates, fraud signals and support contacts before widening access. Agree rollback criteria in advance, such as a failure-rate threshold or a reconciliation break count, and rehearse the rollback once in staging. Expand cohorts only when every agreed metric holds steady for a full cycle.
Set up observability, on-call practice, compliance reviews and a release cadence that limits operational risk. Review incidents weekly. Track business metrics such as payment success rate, reconciliation breaks, dispute turnaround and support volume alongside technical ones. Understand why ongoing app maintenance protects stability, since provider updates, security patches and regulatory changes keep arriving after launch.
The same foundations apply to any end-to-end app development process, whatever the product type. The fintech additions are compliance mapping, partner due diligence, and reconciliation testing. Therefore, plan release one around learning. A narrow product that settles money correctly beats a broad one that does not.
The main fintech app development challenges are regulatory complexity, provider dependency, security threats, legacy integration, data accuracy, and scale. Each has a known engineering answer when addressed at the design stage.
| Challenge | Practical solution |
|---|---|
| Shifting regulations across regions | Configurable policy engine, jurisdiction-aware rules, a named owner for regulatory change |
| Dependence on one provider | Abstraction layer, secondary providers for critical rails, SLAs with exit clauses |
| Fraud and account takeover | Device signals, behavioral analytics, step-up authentication, real-time rules and ML scoring |
| Legacy core integration | Anti-corruption layer, event-based sync, incremental migration instead of big-bang replacement |
| Ledger discrepancies | Immutable double-entry ledger, daily automated reconciliation, break-handling workflows |
| Peak-load scaling | Queue-based processing, horizontal scaling, load tests tied to peak-day projections |
| Slow onboarding | Progressive KYC, pre-filled data via open banking, clear pending-verification status |
Three challenges deserve extra attention.
Teams optimize compliance and forget conversion, and a flow demanding everything upfront loses applicants before they see the product. Tiered onboarding, where limits rise as verification completes, fixes this without weakening controls. Track step-level drop-off to find which check loses the most users and fix that step first.
Banks and insurers still run cores exposing batch files or brittle SOAP services. An anti-corruption layer translates them into clean internal events, keeping legacy quirks out of your domain model.
A single processor outage can stop revenue, so critical rails need a tested fallback, not only a contract clause. Run failover drills quarterly, so the fallback is proven before it is needed. Document the manual procedure for each rail as well, since automation fails in unexpected ways, and operations staff need a clear runbook.
Abstract the dependency, automate the control, and measure the outcome. That pattern solves most of these before production.
A typical fintech app tech stack combines a typed back-end language, a relational database, event streaming, security-strong cloud infrastructure and cross-platform or native mobile frameworks. The best stack is the one your team can operate reliably under audit.
| Layer | Common choices |
|---|---|
| Mobile and web | React Native, Flutter, Swift and Kotlin, React or Angular |
| Back end | Java with Spring, .NET, Node.js with TypeScript, Go, Python for ML services |
| Database | PostgreSQL or SQL Server for ledger data, Redis for caching |
| Messaging | Kafka, RabbitMQ, cloud-native queues |
| Cloud and DevOps | AWS, Azure or GCP, Kubernetes, Terraform, CI/CD with security scanning |
| Security tooling | HSM or cloud KMS, WAF, secrets vaults, SIEM |
| Data and AI | Snowflake, BigQuery or Redshift, feature stores, model serving |
Selection criteria matter more than trends. Transactional guarantees, mature payments and cryptography ecosystem, hiring availability and compliance compatibility. A relational database for the ledger remains the safe default, because ACID guarantees are hard to replace when money is involved.
The approaches for bulding cross platform apps now cover most fintech needs and cut delivery time. Reserve native development for deep device access such as secure enclaves. Pick one primary language across services where possible, because a smaller stack is easier to secure, audit and staff.
Open banking and third-party application integration services give fintech apps access to account data, payment initiation and verification without building each connection from scratch. Done well, they cut onboarding time. Done poorly, they create fragile dependencies.
Plan for the Integration EffortFor fintech API integration, wrap each provider in an internal interface, treat consent as a first-class entity with scope, expiry and revocation, and expect inconsistency in bank API uptime and data quality outside the EU and UK. Monitor provider health with synthetic transactions and automated failover. PSD2 keeps evolving, and US open banking rules remain in flux, so keep data-sharing logic configurable.Integration is where much real effort sits. Budget for it and never assume a sandbox behaves like production. Rate limits, data volumes and error behavior often differ materially once real traffic arrives.
Fintech app development costs typically range from $40,000 to $300,000, depending on app type, workflow complexity, integrations and compliance scope. Most projects take 3 to 12 months and regulated multi-region products can exceed these ranges.
| App type | Approximate cost |
|---|---|
| Investment apps | $50,000 to $150,000 |
| Insurance apps | $40,000 to $200,000 |
| Personal finance apps | $50,000 to $250,000 |
| Lending apps | $40,000 to $150,000 |
| Banking apps | $60,000 to $300,000 |
These reference ranges reflect a first production release. What moves a project within its range:
Jurisdictions, licenses and audit requirements each add controls and evidence work. Launching in one region with a defined license path costs far less than building several regimes at once.
Every extra bank, processor or data provider adds build and test effort, and poorly documented APIs add more. Allow time for sandbox gaps, certification cycles with partners and error handling for each provider's unusual behavior.
Multi-region failover, advanced fraud tooling, and certifications raise costs. Decide the recovery objectives and assurance reports customers will demand, then size infrastructure and audit work to match.
Native iOS, Android and web cost more than one cross-platform build. Start where your users are concentrated and add channels only when usage data justifies the extra testing, release and support overhead each one brings.
Admin and reporting tooling is often a quarter or more of the effort, and underestimating it is a frequent cause of overruns. Operations, risk and support teams need case management, approved manual adjustments, and reports from day one.
Cloud, provider fees, security testing, compliance reviews and maintenance recur yearly. Transaction-based fees scale with volume, so model them against expected growth.
Treat these as a starting point, not a quote. For budgeting beyond fintech, see factors that raise app development cost.
Detailed scoping before development is the most reliable budget control, since it surfaces integration and compliance with unknowns while they are cheap. Reserve contingency of 15 to 20 percent for integration surprises and agree upfront how scope changes are priced.
The right fintech app development company combines proven delivery in regulated environments, compliance and security experience, integration depth with banks and processors, and transparent engagement models. Ask for evidence, not slide decks.
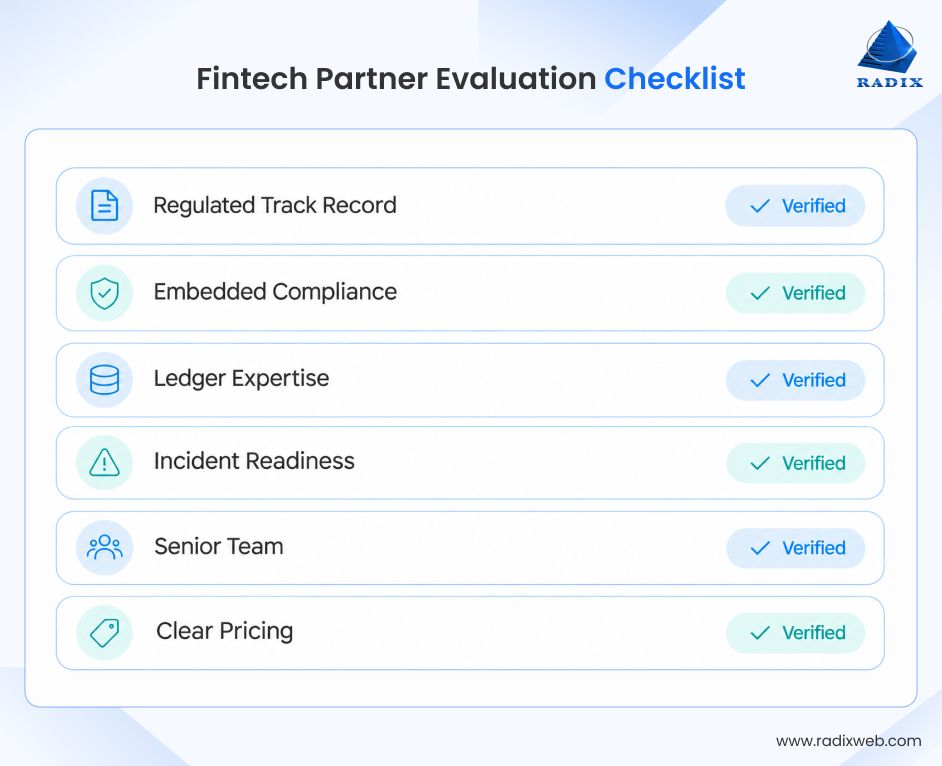
Look for fintech products already live in production, with clear details on license models, regulators involved, audit outcomes and transaction volumes. Case studies that skip these specifics rarely reflect real regulated delivery.
Strong partners embed PCI DSS, SOC 2, GDPR and regional controls into design reviews, pipelines and release checks instead of leaving them to a final audit. They can show sample evidence and how findings are tracked to closure.
The team should explain double-entry ledgers, idempotency, reconciliation and failure handling with confidence, and show how a provider can be replaced without rewriting business logic.
Look for defined on-call coverage, response targets and escalation paths, plus real experience handling a payments incident. Support should continue beyond launch, with clear ownership.
Named senior engineers should stay on the product, backed by low attrition and a clear handover process. This protects continuity when scope grows or priorities shift.
Fintech scope shifts as partner and regulatory details surface. Look for a clear change-request process; sensible contingency and fixed-price offers only after a proper discovery phase.
Red flags include vague compliance answers, no regulated-client references, fixed-price promises without discovery and weak internal security.
A paid discovery phase before the full build shows how a partner thinks and handles ambiguity better than any sales process. Check references from regulated clients and ask them to meet the engineers who will build the product.
Fintech app development trends & stats over the next few years, center on embedded finance, real-time payments, stablecoin and tokenized-asset rails, agentic AI and tighter regulations on data, resilience and AI governance. Modular, compliant platforms will adapt fastest.
Wider market direction shows up in, emerging trends shaping fintech roadmaps and pressure fintech puts on traditional banks.
Design for change. The products that last can swap providers, rules and models without rebuilding the core. Keep a living architecture decision log so the team can revisit choices as regulation and rails change.
AI in fintech app development is now used mainly in fraud detection, credit decisioning, support, document processing and operations automation. The 2027 shift is from standalone models to AI embedded in workflows, with governance built around it.
Constraints matter as much as capability. Credit models need explainability, bias testing, and human override. Training data needs clear consent. Drift needs monitoring, since fraud patterns shift quickly.
Enterprises scoping this can explore tailored AI systems for financial products. Start with one high-volume, well-measured use case, prove the lift, then expand. Measure approval rate, fraud loss and handling time before and after, so the business case rests on data.
Build the Foundation for Your Next Fintech Project with Radixweb
A successful fintech product is decided early; license position, ledger design, compliance architecture and integration strategy. Polish cannot compensate for a weak foundation. Teams that map money flow first, treat security as a platform layer and plan for provider change, ship faster and spend less over the product's life. Radixweb has been engineering enterprise software since 2000, including lending and banking platforms. With custom app development for fintech enterprises, those decisions get tested against real transaction volumes before launch, not after.Start with discovery, a regulatory matrix, and a clear view of the integration landscape. Agree on the license route, the first workflow to launch, and the partners to evaluate before any estimate is finalized. If you are scoping a build, book your no-cost consultation with our fintech specialists, discuss your roadmap and pressure-test the plan. A short working session usually exposes the biggest license and budget risks.
Ready to brush up on something new? We've got more to read right this way.