
Recognized for AI Excellence at 2026 Globee® Awards - Read More
Client Background
SynCore is a SaaS company that owns a pricing-based software platform for managing RFx processes, which include requests for information, proposals, and quotes. Their software helps businesses efficiently handle these tasks by automating the process of collecting and evaluating bids.

Client Location
USA

Industry
SaaS

Project Duration
3+ Months

Engagement Model
Time and Material
The Problem

The client team’s existing setup was mostly manual, with only an automated proof of concept (PoC) pipeline in place. They used Bitbucket for DevOps, but their deployment process was very inconvenient to manage. It depends on version control systems and updates the local branch on a virtual machine without proper packaging or version control.
Essentially, the entire process was like working on a local computer - a branch is pulled to a VM, updated, and then refreshed using PM2 and Nginx to apply changes without downtime. On top of this, database changes had to be shared through Slack, which is not very organized or efficient.
Business Requirements
SynCore’s DevOps team knew that their deployment process was not well-organized. Managing and deploying the software was complex and they had security issues too, with access keys being visible and vulnerable to potential breaches. Their current API setup also limited their ability to switch to a better, more efficient deployment process.
Automating unit tests was also a challenge as their current Bitbucket pipelines weren’t handy for tracking changes. Additionally, there was limited visibility into build metrics and system performance trends, which could benefit from automated insights driven by data analytics and predictive anomaly detection.
Lastly, their entire workflow had to move to an effective process that included better packaging of their software. Ideally, they wanted to serve their UI files from a Content Delivery Network (CDN) to improve performance and manageability, rather than packaging everything together in one place.
They were already working on DevSecOps security scanning and wanted to integrate security earlier in the process. Our role was to help them build a team with the processes and technologies needed to achieve that goal.
Client Feedback

There's a big difference between a team that just does what you ask and one that actually helps you think it through. Radixweb was the latter. Our team's a lot less stressed now, and we barely hear from unhappy clients anymore.
Rather than pushing for a full platform rebuild, we focused on practical, incremental improvements, automation, cleaner data flow, and dashboards that stakeholders use. That approach built trust and kept the engagement productive year after year.

Niketa Parekh
What We Proposed
- Migrate from Bitbucket to Microsoft Azure DevOps with automated CI/CD pipelines to eliminate manual VM deployments.
- Integrate security scanning (SonarQube, OWASP) directly into the pipeline to catch vulnerabilities before production.
- Automate unit testing and compliance monitoring to run with every build instead of manual checks.
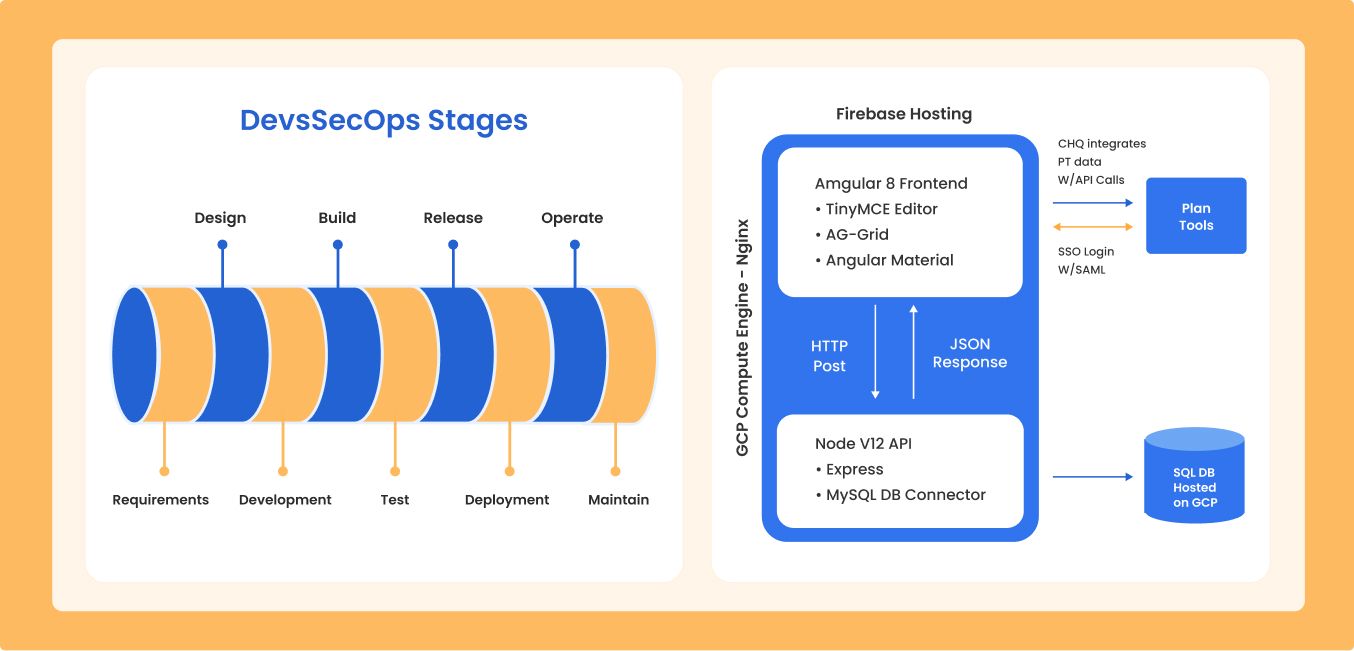
- Separate UI files to Firebase Hosting and CDN to improve performance and reduce packaging complexity.
- Set up telemetry-based monitoring and anomaly detection to replace ad-hoc Slack notifications with real-time visibility.

Project Objectives

Higher-Quality Product
Our top-most goal was to improve the overall quality and security of the software. For that, the software must have fewer bugs and offer better performance so that the product works as intended and meets users’ needs.

Faster Delivery
We wanted to speed up the delivery process so that new features and updates reach users more quickly. The key strategy to achieve this is automating tasks and streamlining the workflow to cut down on delays.

Improved Deployment Frequency
Another task was to increase how often new updates and features are deployed. By building a DevSecOps CI/CD pipeline, the client could release updates more regularly and keep the software up-to-date and relevant.

Fewer Security Incidents
We aimed to reduce the number of problems or incidents that arise in the software. By catching issues earlier and automating processes, we can prevent issues from escalating and ensure smoother operations.

Lower Failure Rate of New Releases
We wanted to minimize the chances of new updates or releases causing problems. By enhancing testing and quality checks, we can reduce the likelihood of errors and ensure new features work correctly.

Faster Recovery Times
If something goes wrong, we need to make the recovery process quicker. For that to happen, the team has a DevSecOps-powered SaaS RFx platform in place to quickly fix issues and get the software back up and running without prolonged downtime.
Book a 30-minute call directly with a senior DevOps engineer to review your current pipeline. You'll get a scoped recommendation on the call.
Key Functionalities
Accessibility Features
To achieve the desired process, we used Microsoft Azure's DevOps tooling solutions with a server agent for builds and deployments. CI/CD and test pipelines were set up with telemetry-based monitoring and anomaly detection, while Firebase Hosting supported the Angular front end. Azure DevOps is secure, enterprise-ready, and enables data-driven insights via its marketplace, while Firebase delivers cost-effective, automated CDN support.
Static Code Analysis
We’ll integrate static code analyzers to help the client team write secure code that forms the architectural backbone of the system. Static Application Security Testing (SAST) tools like SonarQube and TSLint or any tool of their choice would work as an automated part of their development process and help detect and fix potential vulnerabilities early. The setup will be a one-time activity for our team.
Vulnerability Scan
Security testing solutions will be implemented into the development process to check for security issues throughout the pipeline framework for continuous integration and continuous deployment. The team can check the code for bugs and vulnerabilities before it’s released. We’ll set up an OWASP security testing tool for this, and it will be a one-time setup as well.
Unit Tests/Penetration Tests
The client team can write tests to check individual parts of the code. We went for CI/CD pipeline implementation to automate running these tests with each build. Hence, they can check everything before releasing new versions. Our team will handle the setup for this, which will be done just once.
Compliance Testing
In DevSecOps, compliance is about continuously managing and fixing security settings in real time. Instead of just ticking boxes, we’ve made sure they get alerts when any security settings change. This task is optional, and our team can handle it if needed.
Deployment Pipeline
Our team will manage the process of SaaS deployment automation from the final build to the production environment. This involves handling various types of build outputs, such as libraries and bundles. Our team will set up the deployment process once, and their development team will trigger the deployments using this setup.
Business Benefits

Faster Deployments
The deployment time for new features and updates was cut by 57%. Previously it took 5 hours, but now it only takes 2.15 hours. As a result, SynCore has doubled their release frequency. They can now deploy new builds almost 10+ times a month instead of 4.

Improved Code Quality
Automated testing caught >95% of bugs before they reached production. The software now reportedly receives a lot less user-reported issues, from 20 per month to just 1 or 2. This is a significant improvement in code quality.

Upgraded Security
Implementing DevSecOps automation reduced security vulnerabilities by 82%. The number of security incidents dropped from 10 to just 2-3 per quarter – a direct result of running over 450 vulnerability scans and security checks per month.

Higher Uptime
System reliability improved dramatically with DevSecOps pipeline implementation. The current downtime is less than 1% per month, which means out of 720 hours in a month, the system was unavailable for less than 7 hours.
Explore More Case Studies


Get a dedicated DevOps engineer for 80 hours a month to audit your current pipeline and implement one measurable fix. Scope and pricing locked in within 3 business days.